By Shizza Umer
The Advertisement You Never Clicked
Imagine visiting an ordinary website, seeing an advertisement and moving on. You never click it, download anything or enter a password. Yet the advertisement itself could become the doorway into your device.
That is the mechanism described in an investigation published on 15 October 2026 by the University of Toronto’s Citizen Lab, alongside a separate investigation by the ad-security firm Confiant.
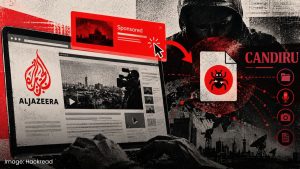
The researchers documented how digital advertising systems were used to identify selected devices and deliver zero-click spyware. Rather than waiting for someone to open a suspicious link, the attack could begin when a targeted ad loaded.
This does not mean everyone who saw the ads was infected. The system was designed to single out chosen targets from everyone else.
Citizen Lab’s director, Ron Deibert, called the findings a “worst-nightmare” scenario and “a recipe for disaster”.
The Isr.eli Companies Behind the Operation
The investigation connects two Isr.eli companies: the Tel Aviv advertising firm Discover-Tech and the spyware maker Candiru, now known as Integrity Labs.
Discover-Tech ran an advertising platform called Controlium. According to Citizen Lab, scripts inside the ads checked each device’s advertising ID and IP address to decide whether it was a target. Selected devices received the attack code. Everyone else received nothing.
Candiru was already known to security researchers. In 2021, the United States placed it on a trade blacklist, and its tools have previously been linked to attacks on journalists.
Neither Discover-Tech nor Candiru responded to requests for comment from multiple news organisations.
The investigation identifies the companies and infrastructure involved. It does not establish which government or client ordered the attacks.
Inside the Al Jazeera Attacks
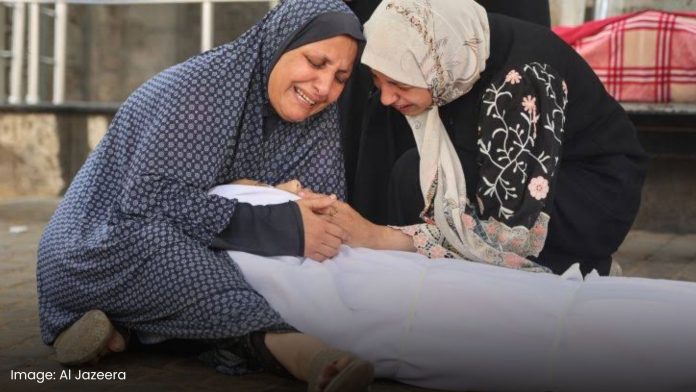
Al Jazeera’s technology team noticed unusual patterns on some journalists’ devices in 2024, and the pattern continued into 2025. The network asked Citizen Lab to investigate.
According to Citizen Lab, at least 45 Windows devices at Al Jazeera were targeted during 2024 and 2025.
According to Al Jazeera, the spyware can collect files, browser data and saved passwords, log keystrokes, take screenshots, record through the microphone and webcam, and extract messages. Researchers have not said which of these capabilities were used on each device.
Al Jazeera said it “condemns the spyware attacks targeting a number of its staff”, called the targeting of journalists an “assault on press freedom” and demanded that those responsible be held accountable.
Al Jazeera was not alone. Citizen Lab detected potentially malicious ads aimed at journalists at up to 18 other news organisations in Isr.el, France, Italy, Australia and Mexico, according to Forbes.
For a newsroom, even one compromised device can endanger confidential sources and expose unpublished work.
A Global Advertising Footprint
The scale went far beyond one newsroom. Citizen Lab analysed nearly four billion ad-bidding records from March to June 2026 and identified about 442 million winning ad impressions.
Ads carrying the firm’s script appeared on more than 120,000 websites and 75,000 apps, reaching devices in 161 countries. Yemen received more bids than any other country, about 457 million.
The firm’s presence was especially heavy in Palestine. “You go to almost any site in Palestine … you find a Discover-Tech ad,” Confiant’s Jerome Dangu told Reuters.
The ads also appeared on networks used by the Pentagon, the International Atomic Energy Agency, the International Criminal Court, the UN, NATO, the European Commission and more than a dozen national governments.
There is an important distinction here. An ad appearing on a network is not proof that the network was hacked, and researchers found no evidence that these institutions were infected. Ad impressions, targeted devices and confirmed infections measure different things.
Approved for Years. Banned Now.
Discover-Tech had been an approved vendor with Google and IAB Europe since 2020.
Google has now removed it for “systematically violating our policies” and added Chrome warnings for sites linked to the firm. IAB Europe suspended it, and the ad platforms Beeswax, Eskimi and Vungle also blocked or paused its access.
Yet the central questions remain unanswered: who ordered the attacks, how many other devices were compromised, and how many similar operations have not yet been found?
The findings expose a dangerous weakness in an advertising system used across the internet. In the wrong hands, an ad can become a delivery mechanism for surveillance software.
And the person viewing it may never know.
Sources
Primary investigation
Additional reporting
- https://www.aljazeera.com/news/2026/10/15/israeli-ad-tech-firm-helped-spy-on-al-jazeera-devices
- https://www.aljazeera.com/video/newsfeed/2026/10/15/israeli-ad-firm-helped-infect-spyware-into-al-jazeera-devices
- https://www.thenationalnews.com/news/mena/2026/10/16/israeli-company-used-online-ads-to-run-spy-operation-against-hundreds-of-millions-of-people/
- https://www.newarab.com/news/israeli-ad-firm-helped-spyware-target-al-jazeera-journalists
- https://ca.news.yahoo.com/israeli-firm-used-ads-enable-002312677.html
- https://www.forbes.com/sites/thomasbrewster/2026/10/15/israeli-spyware-ads-target-journalists/
- https://thenextweb.com/news/citizen-lab-targeted-ads-spyware
- https://www.middleeasteye.net/news/israeli-spyware-targeted-hundreds-millions-through-zero-click-ads-researchers-find
- https://newscord.org/article/citizen-lab-says-discover-tech-used-targeted-online-ads-to-deliver-zero-click-sp–Story_20261015_Israeliadtechfirmhel44803e0f